
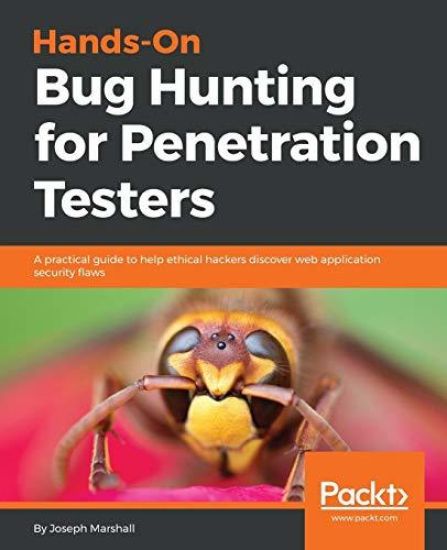
Hands-On Bug Hunting for Penetration Testers – hinnat ja saatavuus
A practical guide to help ethical hackers discover web application security flaws
Kirjafiili on kirjojen hintavertailu. Löydä halvin hinta 27 kirjakaupasta. Hintavertailu koskee ISBN-tunnusta 9781789344202 (nidottu).
Kirjan kuvaus
Detailed walkthroughs of how to discover, test, and document common web application vulnerabilities. Key FeaturesLearn how to test for common bugsDiscover tools and methods for hacking ethicallyPractice working through pentesting… Näytä koko kuvaus Piilota kuvaus
Detailed walkthroughs of how to discover, test, and document common web application vulnerabilities. Key FeaturesLearn how to test for common bugsDiscover tools and methods for hacking ethicallyPractice working through pentesting engagements step-by-stepBook DescriptionBug bounties have quickly become a critical part of the security economy. This book shows you how technical professionals with an interest in security can begin productively—and profitably—participating in bug bounty programs. You will learn about SQli, NoSQLi, XSS, XXE, and other forms of code injection. You’ll see how to create CSRF PoC HTML snippets, how to discover hidden content (and what to do with it once it’s found), and how to create the tools for automated pentesting workflows. Then, you’ll format all of this information within the context of a bug report that will have the greatest chance of earning you cash. With detailed walkthroughs that cover discovering, testing, and reporting vulnerabilities, this book is ideal for aspiring security professionals. You should come away from this work with the skills you need to not only find the bugs you're looking for, but also the best bug bounty programs to participate in, and how to grow your skills moving forward in freelance security research. What you will learnChoose what bug bounty programs to engage inUnderstand how to minimize your legal liability and hunt for bugs ethicallySee how to take notes that will make compiling your submission report easierKnow how to take an XSS vulnerability from discovery to verification, and report submissionAutomate CSRF PoC generation with PythonLeverage Burp Suite for CSRF detectionUse WP Scan and other tools to find vulnerabilities in WordPress, Django, and Ruby on Rails applicationsWrite your report in a way that will earn you the maximum amount of moneyWho this book is forThis book is written for developers, hobbyists, pentesters, and anyone with an interest (and a little experience) in web application security.
Kirjan tiedot
Vertaa kirjan ”Hands-On Bug Hunting for Penetration Testers” hintoja
Vertaa tuotteen hintaa ja arvioitua kokonaishintaa toimitettuna. Kaikki hinnat koskevat ISBN-tunnusta 9781789344202.
Hintoja ei päivitetty automaattisesti. Voit hakea ajantasaiset hinnat painamalla Hae hinnat.

Booky

Suomalainen

Kansallinen Kirjakauppa

Prisma

Finlandia Kirja

Fantasiapelit

Vinhan kirjakauppa

CDON

Kustantamo S&S
Kennys.ie

Kristillinenkirjakauppa.fi
Sacrum

Adlibris

BookOutlet.fi

Kirja.fi

Rosebud
Tälle kirjalle ei ole tällä hetkellä vahvistettua hintaa. Tarkista tilanne myöhemmin uudelleen.
Hintoja ei ole vielä päivitetty.
Hälytys tallennettu!
Ilmoitamme, kun hinta laskee.
Saat sähköpostin, kun hinta laskee asettamaasi rajaan tai sen alle.
Hands-On Bug Hunting for Penetration Testers – hintahistoria
Seuraamme kirjan Hands-On Bug Hunting for Penetration Testers hintakehitystä kirjakaupoissa. Taulukosta näet viime kuukausien alimmat hinnat.
Alin hinta kauppoittain
Kunkin kaupan alin hinta viimeisten 90 päivän aikana.
Hintahistoriaa ei ole vielä kerätty tälle kirjalle.
Hinnat ilman toimituskuluja.