
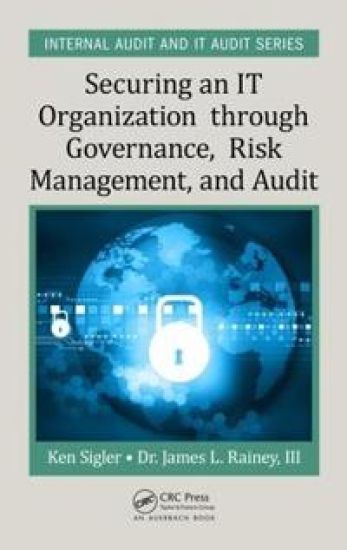
Securing an IT Organization through Governance, Risk Management, and Audit – hinnat ja saatavuus
Kirjafiili on kirjojen hintavertailu. Löydä halvin hinta 27 kirjakaupasta. Hintavertailu koskee ISBN-tunnusta 9781498737319 (sidottu).
Kirjan kuvaus
Past events have shed light on the vulnerability of mission-critical computer systems at highly sensitive levels. It has been demonstrated that common hackers can use tools and techniques downloaded from the Internet to attack government… Näytä koko kuvaus Piilota kuvaus
Past events have shed light on the vulnerability of mission-critical computer systems at highly sensitive levels. It has been demonstrated that common hackers can use tools and techniques downloaded from the Internet to attack government and commercial information systems. Although threats may come from mischief makers and pranksters, they are more likely to result from hackers working in concert for profit, hackers working under the protection of nation states, or malicious insiders. Securing an IT Organization through Governance, Risk Management, and Audit introduces two internationally recognized bodies of knowledge: Control Objectives for Information and Related Technology (COBIT 5) from a cybersecurity perspective and the NIST Framework for Improving Critical Infrastructure Cybersecurity (CSF). Emphasizing the processes directly related to governance, risk management, and audit, the book provides details of a cybersecurity framework (CSF), mapping each of the CSF steps and activities to the methods defined in COBIT 5. This method leverages operational risk understanding in a business context, allowing the information and communications technology (ICT) organization to convert high-level enterprise goals into manageable, specific goals rather than unintegrated checklist models. The real value of this methodology is to reduce the knowledge fog that frequently engulfs senior business management, and results in the false conclusion that overseeing security controls for information systems is not a leadership role or responsibility but a technical management task. By carefully reading, implementing, and practicing the techniques and methodologies outlined in this book, you can successfully implement a plan that increases security and lowers risk for you and your organization.
Kirjan tiedot
Vertaa kirjan ”Securing an IT Organization through Governance, Risk Management, and Audit” hintoja
Vertaa tuotteen hintaa ja arvioitua kokonaishintaa toimitettuna. Kaikki hinnat koskevat ISBN-tunnusta 9781498737319.
Hintoja ei päivitetty automaattisesti. Voit hakea ajantasaiset hinnat painamalla Hae hinnat.

Booky

Suomalainen

Kansallinen Kirjakauppa

Prisma

Finlandia Kirja

Fantasiapelit

Vinhan kirjakauppa

CDON

Kustantamo S&S
Kennys.ie

Kristillinenkirjakauppa.fi
Sacrum

Adlibris

BookOutlet.fi

Kirja.fi

Rosebud
Tälle kirjalle ei ole tällä hetkellä vahvistettua hintaa. Tarkista tilanne myöhemmin uudelleen.
Hintoja ei ole vielä päivitetty.
Hälytys tallennettu!
Ilmoitamme, kun hinta laskee.
Saat sähköpostin, kun hinta laskee asettamaasi rajaan tai sen alle.
Securing an IT Organization through Governance, Risk Management, and Audit – hintahistoria
Seuraamme kirjan Securing an IT Organization through Governance, Risk Management, and Audit hintakehitystä kirjakaupoissa. Taulukosta näet viime kuukausien alimmat hinnat.
Alin hinta kauppoittain
Kunkin kaupan alin hinta viimeisten 90 päivän aikana.
Hintahistoriaa ei ole vielä kerätty tälle kirjalle.
Hinnat ilman toimituskuluja.